GitHub security
GitHub can screen npm packages before an agent installs them
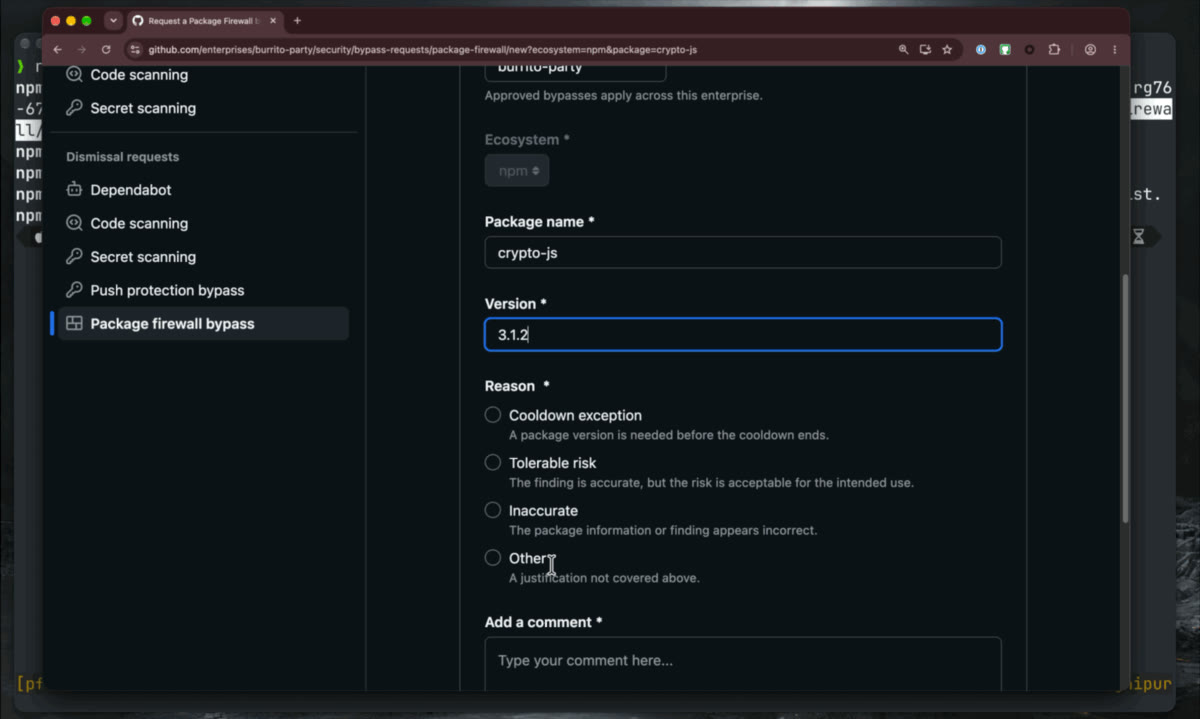
A frame from GitHub's demo shows the exception request for a blocked npm package. View official source ↗
- What changed
GitHub’s package firewall sits between a runner or coding agent and npm. Admins set policy; configured endpoints send package requests through it before installation.
- Why it matters
A malicious package can run code during installation. This gives teams another point to stop it, but an endpoint that still calls npm directly is outside the firewall. The preview covers npm on Enterprise Cloud.
- What to do
Try it on one test runner. Confirm the runner uses the firewall, trigger a policy block, and document the exception path. The preview is free; GitHub says billing will be metered after general availability.
OpenAI API
A longer cache can help when requests are hours apart
| Cache lifetime | Write rate | Best fit |
|---|---|---|
| 30 minutes | 1.25× input rate | Closely spaced calls |
| 12 hours | 2.5× input rate | Stable context reused later |
- What changed
The Responses API now offers a 12-hour minimum cache lifetime for shared instructions, tools, and reference text. A longer-lived write costs twice as much as a 30-minute write.
- Why it matters
Teams can reuse a large stable prompt across work sessions. The saving depends on actual cache hits; paying more to write a prefix once may cost more if nobody reuses it.
- What to do
Put only stable material before the cache breakpoint. Compare real cache-write and cached-read tokens over a day with the default lifetime before changing production traffic.
GitHub security
Copilot can draft fixes for code scanning alerts
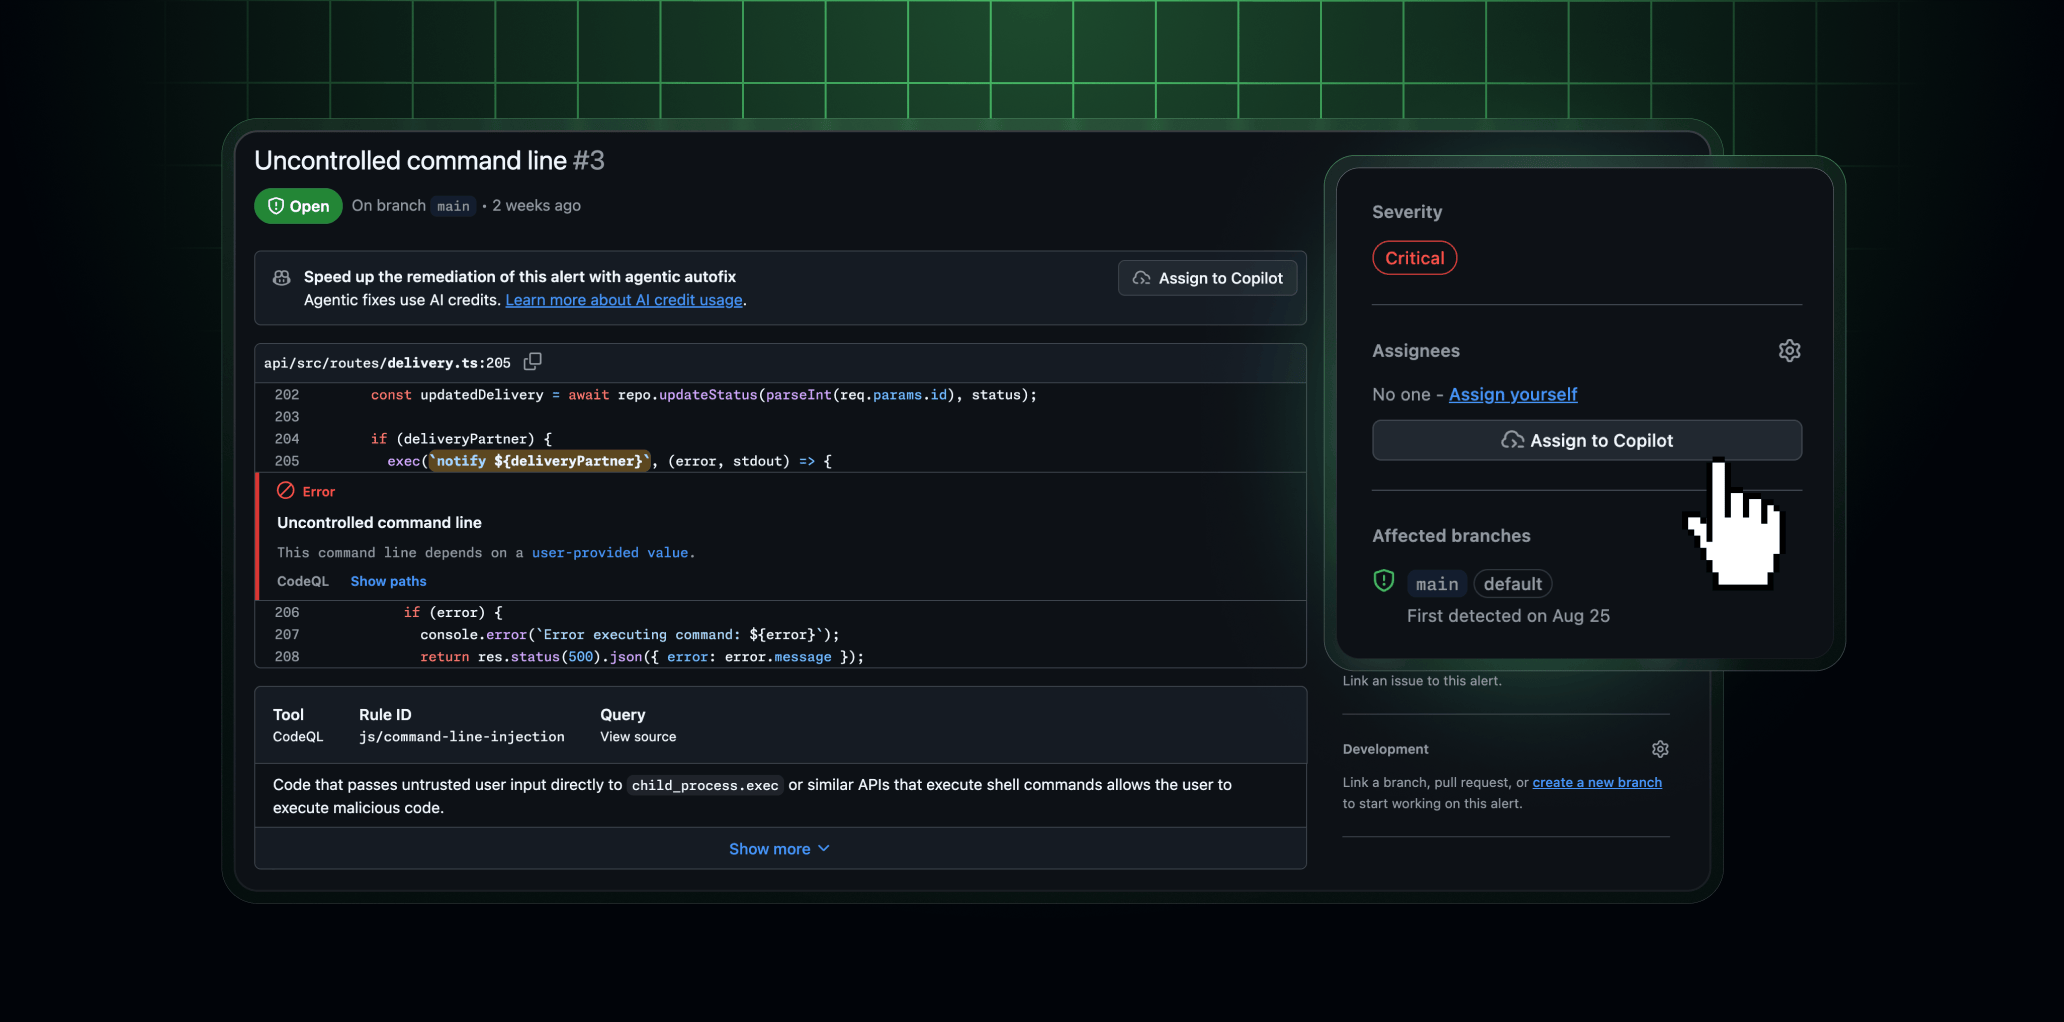
GitHub's release image shows the action on a code scanning alert. View official source ↗
- What changed
Agentic autofix explores relevant code, proposes a fix, reruns CodeQL, and opens a draft pull request. It can take up to 25 default-branch alerts in one request.
- Why it matters
Security findings can move into a reviewable patch. Access requires GitHub Code Security or Advanced Security on Enterprise Cloud, admin enablement, and a Copilot billing method. AI Credits and Actions minutes apply.
- What to do
Assign one lower-risk alert. Read the diff and CodeQL result, run your normal tests, and keep the pull request in human review before merging.
GitHub Copilot
Gemini 4 Argon is now selectable in Copilot
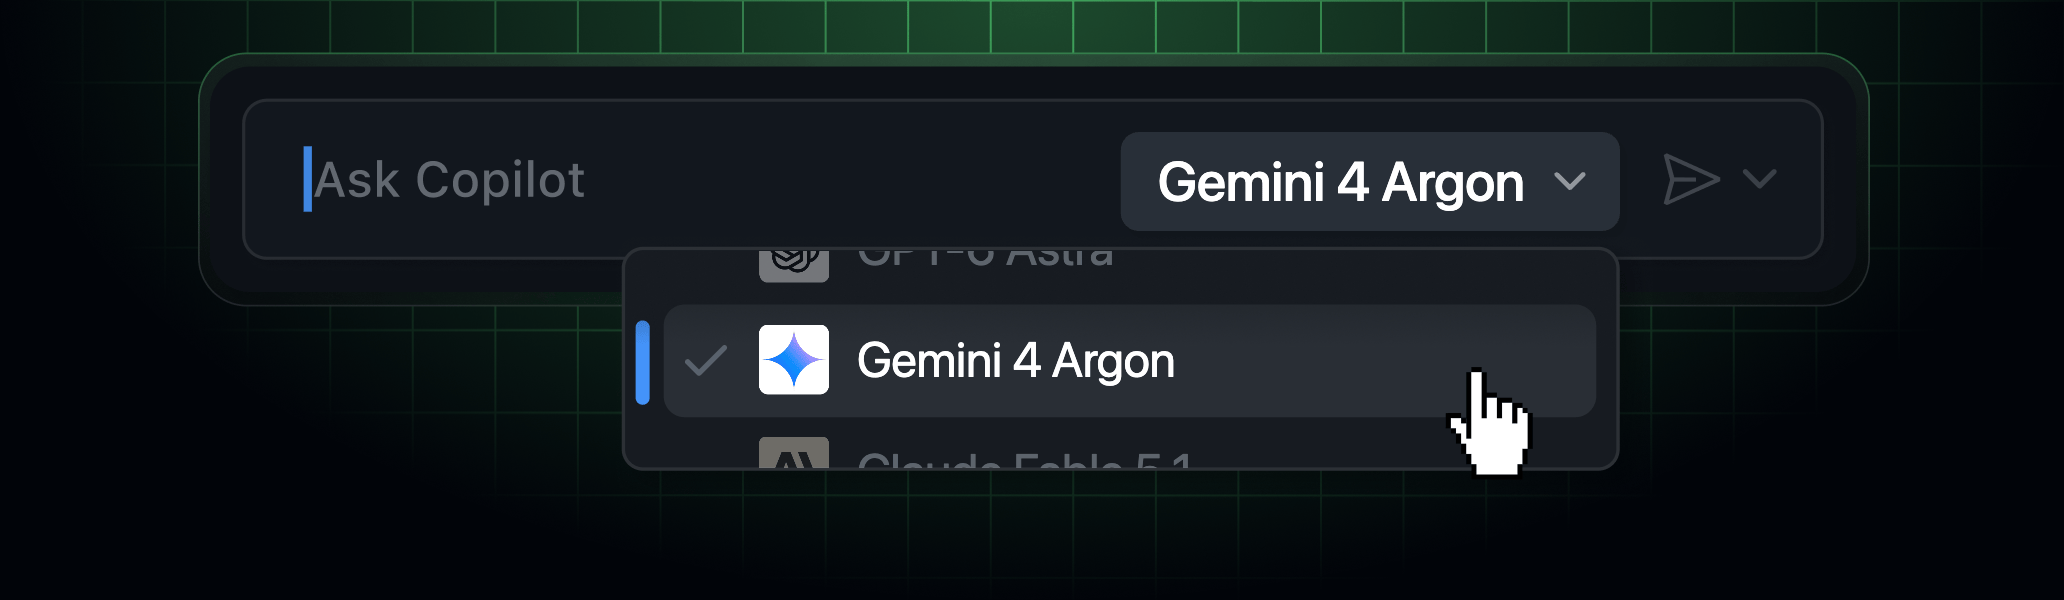
GitHub's release image shows Argon in the Copilot model picker. View official source ↗
- What changed
Gemini 4 Argon has moved from the limited access we covered in Signal 008 to general availability in GitHub Copilot. It is rolling out across major IDEs, Copilot CLI, the coding agent, and the Copilot app.
- Why it matters
Pro+, Max, Business, and Enterprise users get a practical way to test it on coding work. GitHub bills it at provider list pricing under usage-based billing; business admins can set model policy.
- What to do
Check whether it appears in your picker. Run a task you have already solved, compare the code and tests with your current model, and watch usage before making it a default.
OpenAI Agents API
Hosted agents can now make editable office files
| Hosted tool | File work |
|---|---|
| Artifact SDK | Create and edit files |
| Built-in skills | Sheets, slides, Word docs |
- What changed
OpenAI-hosted sandboxes in the Agents API now include the Artifact SDK and document skills. Builders can give an agent tools to create and edit common office files without provisioning those tools themselves.
- Why it matters
A document task can finish with an editable file. The release note says nothing about whether the content, formulas, or layout are correct for your use case.
- What to do
Run one repeatable document task in a test sandbox. Open the result in its native app, check the structure and figures, and record the agent's time and cost.
Also since the last issue
Useful updates
Anthropic's agent-behaviour report
Anthropic reported four unintended action patterns from evaluations and internal use on October 9. It says known real-world impact was minimal. Treat it as a reason to test tool boundaries, not a customer incident.
Open-source license checks
GitHub made enterprise license compliance generally available on October 16. It can block a pull request when a changed dependency breaks policy.
Copilot model policy API
GitHub added policy endpoints on October 19 for enterprise, team, app, and organization model access.
One workflow to try
Measure the longer cache on real traffic
Choose one stable prompt prefix used throughout a workday. Log writes, hits, input tokens, and total cost with the 30-minute setting. Then test 12 hours on the same kind of traffic. Keep it only if the bill and hit rate improve.
Term of the week
Cache write
A cache write stores a prompt prefix for later requests. It has an upfront token charge. A later matching request can read that prefix at a lower rate, but the saving only appears when it actually hits the cache.